About
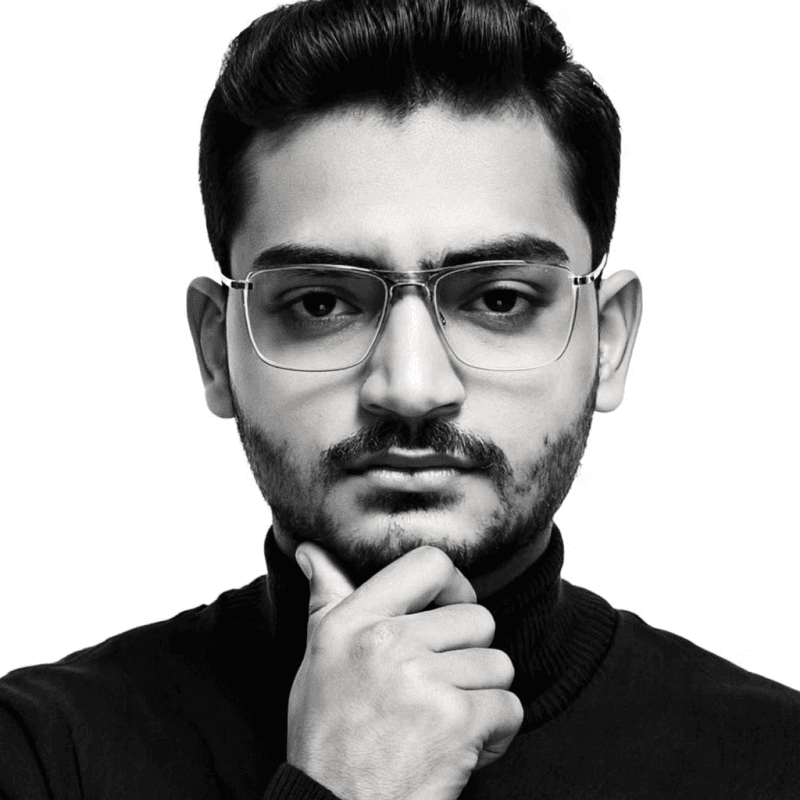
Hi, I'm Shahrooz Mehmood
I'm a senior DevSecOps and cloud infrastructure engineer helping engineering teams automate delivery, secure their pipelines and run reliable infrastructure — with hands-on work in your repositories, not slide decks.
- DevOps & CI/CD
- DevSecOps
- Cloud & platform
Background
Building and securing delivery infrastructure.
Where I come from
Hands-on across the delivery stack
My career has been spent across DevOps, DevSecOps and cloud infrastructure — designing CI/CD pipelines, automating infrastructure with Terraform and Ansible, running containerized workloads on Kubernetes, and integrating security tooling into the software delivery lifecycle.
What I focus on
Security built into delivery
My focus is on DevSecOps practices: security automation, software supply-chain security with tools such as Snyk, and the pipelines and infrastructure that support them.
Who I help
Senior expertise, without the full-time hire
Through this independent practice I work with startups and growing engineering teams — SaaS, fintech, healthtech and AI companies — that need senior hands-on expertise without the time and cost of a full-time hire.
DevOps & CI/CD
Reusable pipelines, release automation and GitOps that make deployments routine.
DevSecOps
Scanning, secrets management and supply-chain security built into delivery.
Cloud & platform
Kubernetes, Terraform and observability on AWS, Azure and GCP.
Teams I love working with
- SaaS
- Fintech
- Healthtech
- AI startups
Remote-first, with scheduled working-hour overlap for teams in the UK, Europe, the Middle East, North America and Australia.
Consulting approach
How I work.
Engineering-first problem-solving
Start from evidence — logs, pipelines, configs and metrics — and find the root cause before proposing tools.
Automation and repeatability
If it has to be done twice, it should be code: pipelines, Terraform, Ansible, Helm and documented runbooks.
Secure by design
Security controls are part of the architecture from day one — least privilege, managed secrets and scanning in CI/CD.
Practical over complex
The simplest solution that meets your requirements. Complexity has an ongoing cost your team will pay.
Documentation and knowledge transfer
Clear docs, diagrams and walkthroughs so your team can operate and extend everything that's built.
Collaboration across teams
Working alongside developers, operations and security — DevOps is a way of working, not a separate silo.
Technology ecosystem
Hands-on across the stack.
Cloud
- AWS
- Microsoft Azure
- Google Cloud (GCP)
Containers & orchestration
- Docker
- Kubernetes
- Helm
CI/CD
- Jenkins
- GitHub Actions
- GitLab CI
- GitOps workflows
Infrastructure as Code
- Terraform
- Ansible
Security
- Snyk
- SAST & SCA
- Container & IaC scanning
- Secrets management
- Supply-chain security
Observability
- Prometheus
- Grafana
- ELK stack
- Alerting & SLOs
You'll talk directly with Shahrooz Mehmood
Let's talk about your infrastructure.
Book a free 30-minute discovery call. You'll leave with an honest view of what to fix first — whether or not we end up working together.
- Free 30-minute call
- No obligation, no hard sell
- Personal reply within two business days